

Dating site eHarmony has confirmed user passwords were leaked in a massive cache uploaded to the internet this week.
The passwords did not contain account usernames, according to the adult dating company.
"After investigating reports of compromised passwords, we have found that a small fraction of our user base has been affected," the company said on its blog.
The passwords were contained in the same dump that exposed potentially 6.5 million LinkedIn users.
News broke about the leak of unsalted LinkedIn passwords after user dwdm uploaded the stolen cache to the cryptographic boffin web site insidepro.
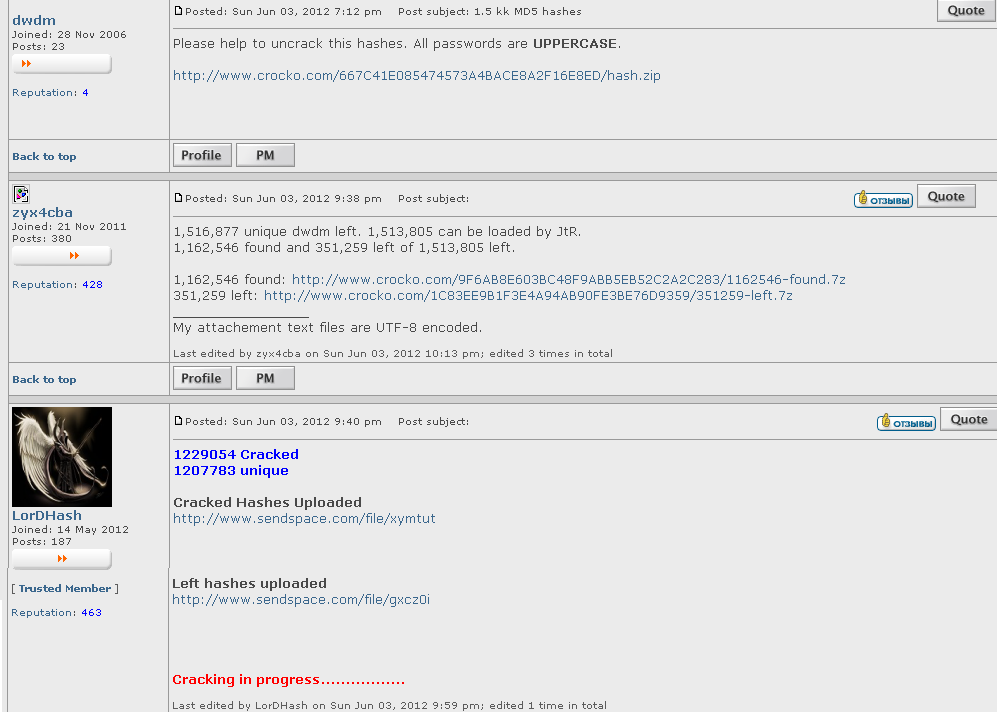 |
Password crackers quickly got to work assisting dwdm to break the SHA-1 cryptographic function.
The words eHarmony and harmony were cited in a second list on the web site but it remained unclear from where the passwords were stolen.
User dwdm did not respond to questions by SC Magazine about the origins of the cache.
EHarmony has reset passwords for "affected" accounts




 Cloud Resilience Summit
 iTnews Benchmark Security Awards 2026
 iTnews State of Security Breakfast Sydney
 iTnews Executive Retreat - Security Leaders Edition - VIC






