

The authors of an old Windows Trojan, DarkComet Remote Access Tool, claim to be working on one for MacOS X systems, called DarkCometX.
DarkComet-RAT’s (Remote Administration Tool) website explains that the Windows tool was designed to make (sic) “hundreds of functions stealthly and remotely without any kind of autorisation in the remote process.”
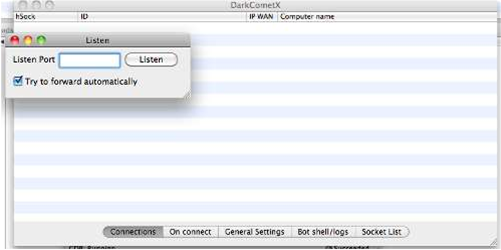
Sophos security adviser Chester Wisniewski earlier this week heralded the rare discovery of a new backdoor Trojan designed for MacOS X systems.
Wisniewski had suggested the origins for “Blackhole Remote Access Trojan (RAT)” for MacOS X could be found in DarkComet-RAT.
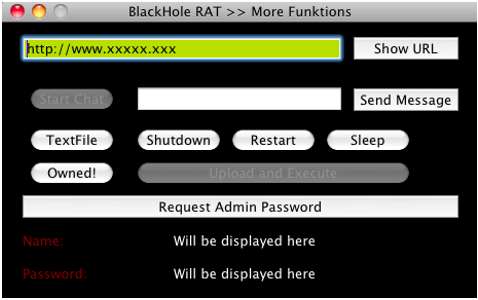
Blackhole RAT’s functions included issuing restart and shutdown commands and running arbitrary shell commands amongst others.
The author of DarkComet-RAT however took exception to Wisniewski’s classification, adding that the rightful heir to its Windows parent was still under development and had a better interface.
“While the BlackHole RAT Trojan seems to be copying the behavior of DarkComet, the lack of functionality and the unsophisticated user interface clearly offended the author,” Wisniewski said.
While the functionality that DarkComet-RAT describes could lend itself to nefarious activities, Wisniewski noted that technically, it is not illegal to write a Trojan.
“It's all in what you do with it,” he said.
(Image courtesy Sophos)




 Cloud Resilience Summit
 iTnews Benchmark Security Awards 2026
 iTnews State of Security Breakfast Sydney
 iTnews Executive Retreat - Security Leaders Edition - VIC






