
Microsoft has published extensive information on new malware it calls FoggyWeb, deployed by Russia-linked threat actors Nobelium who are said to be behind the devastating SolarWinds supply chain attack on corporate and government IT systems worldwide.
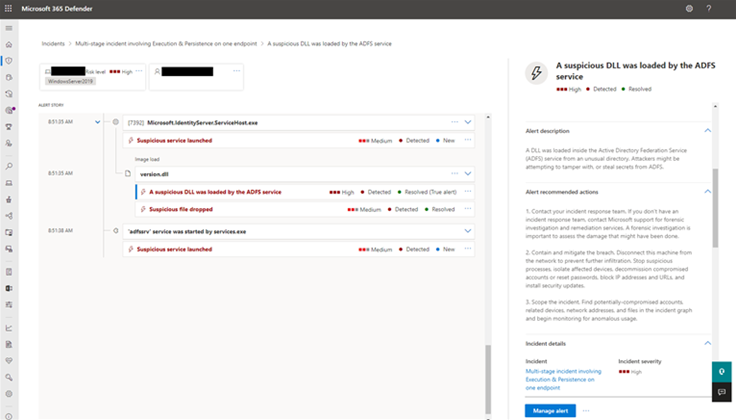
FoggyWeb is backdoor used against Active Directory Federation Services servers, which provide single sign-on for users.
The malware can be used to remotely exfiltrate sensitive information from AD FS servers compromised by Nobelium, Microsoft's Threat Intelligence Centre said.
This includes the AD FS server configuration database, decrypted token-signing and decryption certificates.
FoggyWeb can also receive further malware from Nobelium command and control servers, and run these on compromised AD FS instances.
Customers believed to be attacked by Nobelium and FoggyWeb have been alerted by Microsoft, which recommends that AD FS users take a range of measures to secure their servers.
The company said FoggyWeb is detected by its Defender 365 anti-malware utility.






 Sydney Cloud & Datacenter Convention 2026
 iTnews Executive Retreat - Security Leaders Edition
 Can Testing Keep Up? Quality in the Age of Accelerating Delivery
 iTnews Resilience, Rewired Breakfast
 RIMPA Live Convention 2026



