
Key points
- Citrix has disclosed CVE-2026-107406, a critical memory overflow in NetScaler ADC and Gateway builds that patched last month's exploited flaws, scoring 9.5 on CVSS v4.0.
- Appliances configured for SAML single sign-on as an identity provider, service provider, or both, depending on build, are exposed to remote code execution or denial of service, with no workaround listed.
- It marks the third NetScaler security bulletin in under a fortnight and the fourth SAML-related flaw in NetScaler since March.

Citrix has disclosed yet another critical vulnerability in its NetScaler Application Delivery Controller (ADC) and NetScaler Gateway appliances, this time in the builds that closed last month's actively exploited flaws.
Tracked as CVE-2026-107406, a memory overflow can lead to remote code execution or denial of service on appliances configured for SAML (Security Assertion Markup Language) single sign-on.
It carries a CVSS v4.0 base score of 9.5 out of 10.0 and is rated critical.
"We strongly urge affected customers to review the advisory and upgrade impacted NetScaler instances to the recommended versions as soon as possible," Citrix said.
Which appliances are exposed depends on the build they run.
On builds 14.1-73.37 to 14.1-73.41 and 13.1-64.23 to 13.1-64.28, along with their FIPS and NDcPP equivalents, the flaw applies only when the appliance acts as a SAML identity provider (IdP).
Those are the builds Citrix shipped in late September to fix CVE-2026-88771 through CVE-2026-88778, two of which had already been exploited.
Earlier builds are vulnerable when configured as either a SAML IdP or a SAML service provider (SP).
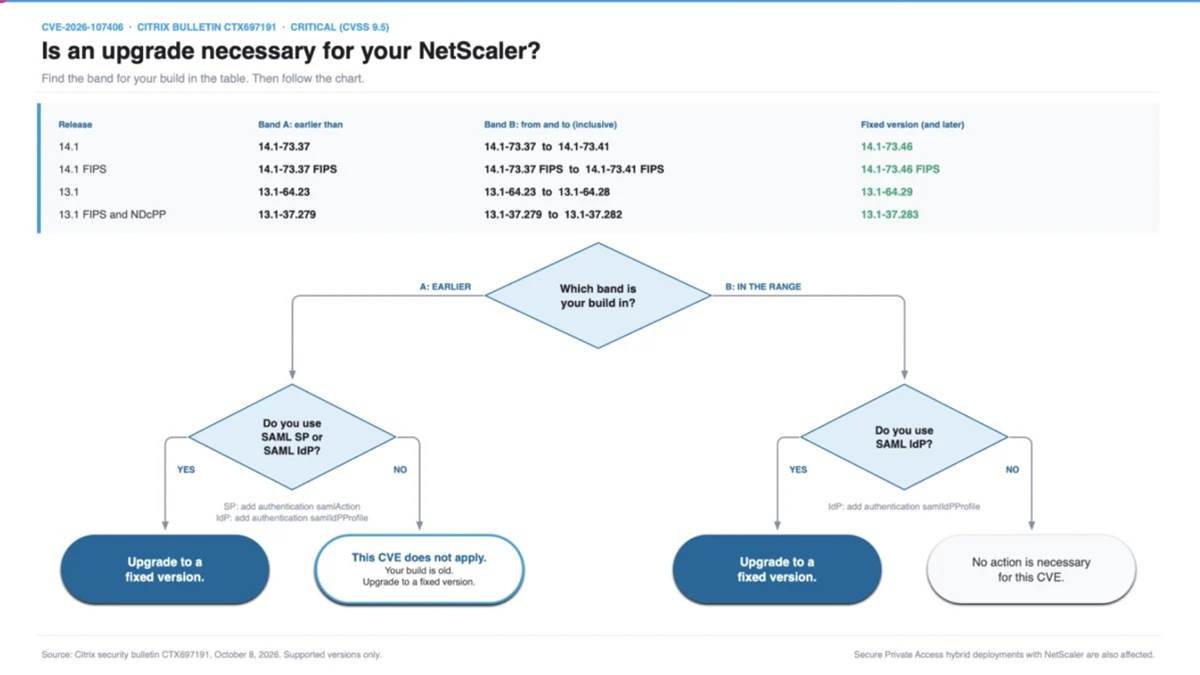
Organisations that moved quickly to patch the September flaws, and that use NetScaler as an identity provider, now have to upgrade again.
The CVE record lists builds before 14.1-73.46 and 13.1-64.29 as affected.
Secure Private Access hybrid deployments that use NetScaler are also in scope.
Citrix-managed cloud services and Citrix-managed Adaptive Authentication are not, as Citrix updates those itself.
Administrators can check their exposure by searching the appliance configuration for "add authentication samlIdPProfile", which indicates IdP mode, or "add authentication samlAction", which indicates SP mode.
The bulletin lists no workaround.
"There's yet another Citrix Netscaler vuln (new patch today) which allows unauth RCE," security researcher Kevin Beaumont said.
It is the third NetScaler security bulletin in less than a fortnight.
The first, on September 27, covered eight vulnerabilities, two of which, CVE-2026-88771 and CVE-2026-88772, had been exploited as zero-days.
On October 3, Citrix disclosed CVE-2026-88779, a SAML flaw that attackers had exploited to knock appliances offline.
Researchers at security vendor watchTowr, who reproduced that bug, reportedly suspect the crashes were deliberate, designed to speed up exploitation of CVE-2026-88771.
"As of the publication of the bulletin, Citrix is not aware of any unmitigated exploits of this vulnerability," the company said.
The CVSS vector also rates attack complexity as high, suggesting exploitation is not trivial, although no authentication or user interaction is required.
SAML handling has become a recurring weak point for NetScaler this year.
In March, Citrix patched CVE-2026-3055, a memory overread affecting appliances configured as SAML IdPs, which the United States Computer and Infrastructure Security Agency (CISA) added to its Known Exploited Vulnerabilities (KEV) catalogue a week later.
CVE-2026-8451, another memory overread bug disclosed on June 30, was found for the same configuration, with honeypot operator Lupovis observing exploitation attempts within roughly 24 hours.
With CVE-2026-88779 and now CVE-2026-107406, that makes four SAML flaws in NetScaler since March.




 iTnews Resilience, Rewired Breakfast
 RIMPA Live Convention 2026
 What’s Next?
 iTnews Benchmark Security Awards 2026
 iTnews State of Security Breakfast Sydney






