The method scans for multiple un-patched Microsoft vulnerabilities in an aim to install a back-door Trojan, according to Joel Camissar managing director A/NZ at Websense.
“Rather than looking for one exploit – which is the norm - it looks for several and hones in on one to then install a Trojan horse,” said Camissar.
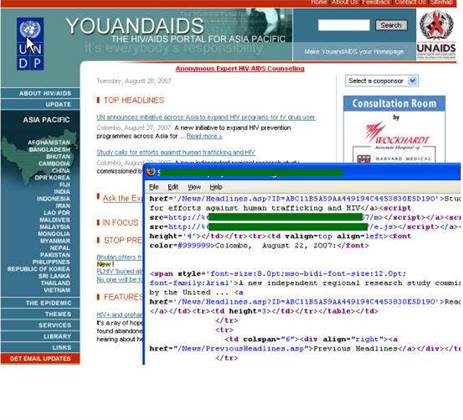
“When the Web site is visited, a malicious JavaScript file (e.js) is executed. Site visitors infected with this malicious code will have a Trojan downloaded and backdoor installed on their desktops,” according to a Websense advisory.
First discovered on 17th August, the technique was used to attack a prominent Indian bank and a US biotechnology company, said Camissar.
“And this campaign is hosted by the same group,” he added.




 HPE Networking Day Sydney
 iTnews Resilience, Rewired Breakfast
 RIMPA Live Convention 2026
 iTnews Benchmark Security Awards 2026
 iTnews State of Security Breakfast Sydney