

Popular password manager Lastpass has plugged bugs in its browser extensions for Google Chrome and Mozilla Firefox that allow attackers to steal passwords and execute arbitrary code.
The vulnerabilities were discovered by Google's Project X security researcher Tavis Ormandy, who reported them to Lastpass.
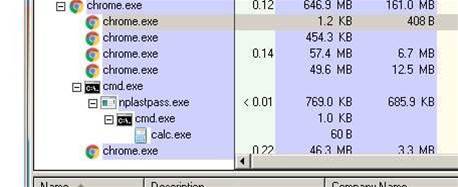
He originally discovered a remote code execution and password stealing flaw in the version 4.1.42 browser extension for Chrome and Firefox and reported it to Lastpass, with a proof of concept exploit that comprised two lines of Javascript.
The flaw requires the Lastpass binary component plugin, which is installed by default for the Lastpass browser extensions in Microsoft's Internet Explorer and Mozilla Firefox, but not in Google Chrome.
Lastpass patched that vulnerability, but soon after, Ormandy reported that he had found two further bugs.
One that allows password stealing was reported in 2015, and received an incomplete fix. Ormandy said exploiting that bug was "not trivial because of the weird context".
A second extension bug could be exploited to open non-websafe browser links, and allow malicious sites to read user credentials silently.
The flaws were fixed in less than 24 hours, and Ormandy commended Lastpass for being quick to act. The company said there was no indication that the vulnerabilties are being exploited in the wild.
Users are advised to upgrade their browser extensions to Firefox: 4.1.36a, Chrome: 4.1.42.82, Edge: 4.1.30, and Opera: 4.1.28, Lastpass said.




 iTnews State of Security Breakfast Sydney
 iTnews Executive Retreat - Security Leaders Edition - VIC
 Mid-Market Summit









