

Sixty percent of exploits target vulnerabilities that are more than two years old according to research.
The US security firm Solutionary's Security Engineering Research Team (SERT) examined cybercrime forums over the last three months as part of its latest research.
The findings indicated individuals and organisations were not adequately applying security patches and could therefore fall victim to attacks against old flaws.
It also found 70 percent of exploits were developed in Russia, and only 7.7 percent crafted in China and 3.9 percent in Brazil. The remaining 19.2 percent could not be determined.
"This data also indicates organisations should not only address zero-day vulnerabilities, but also address missing patches to ensure past vulnerabilities have been remediated," the authors wrote in the report (pdf).
Malware caught less than a third of infections, according to the research.
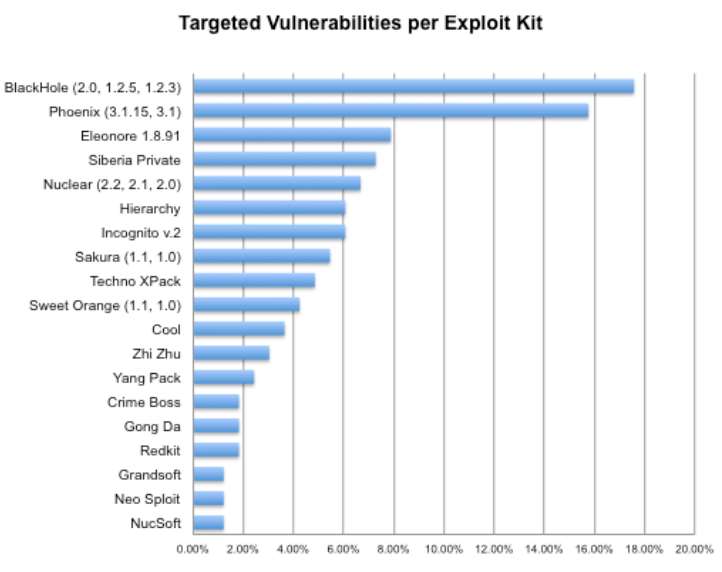
JavaScript was used in 30 percent of collected malware samples for redirection, obfuscation and encryption, including the prolific BlackHole exploit kit which also targeted known vulnerabilities in Adobe Reader and Flash.
More than 18 percent of collected malware samples were linked to the kit.




 iTnews State of Security Breakfast Sydney
 iTnews Executive Retreat - Security Leaders Edition - VIC
 Mid-Market Summit









