

Microsoft is warning that its security intelligence service is seeing a phishing campaign currently targeting hundreds of organisations.
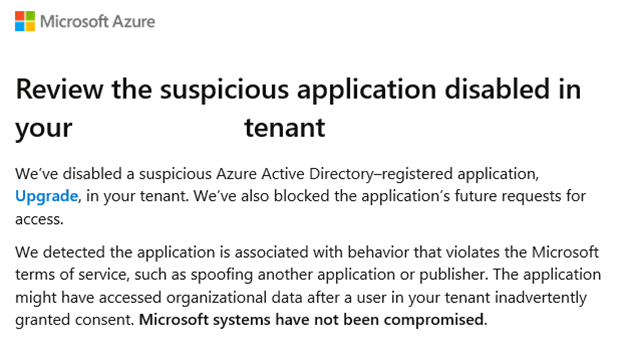
An app named "Upgrade" abuses OAuth request links, and Microsoft said its machine learning technology picked up on this suspicious behaviour.
Users are asked to grant consent to "Upgrade" which would then read their emails as well as write them, and create inbox rules like forwarding all or specific messages to another account to exfiltrate data.
OAuth or Open Authorisation is an open standard access delegation method that lets websites share information without revealing users' passwords.
The attack was reported to Microsoft by a pseudonymous security researcher called TheAnalyst, who said it targeted users for a month.
"Upgrade" is signed by Cardthartic LLC, with the attacker using the viox.dev domain as well, TheAnalyst noted.
Microsoft has deactivated the app in Azure Active Directory, and notified affected customers.
It is not yet known who is behind the phishing attack.




 iTnews State of Security Breakfast Sydney
 iTnews Executive Retreat - Security Leaders Edition - VIC
 Mid-Market Summit









